Local compute
Private Wi-Fi access point, browser UI, streaming DEFLATE, AES-256-GCM, randomness, hashing, and storage control.
 TETHERED UNICORNLABS
FOUNDERS PROTOTYPE · FLAGSHIP HARDWARE
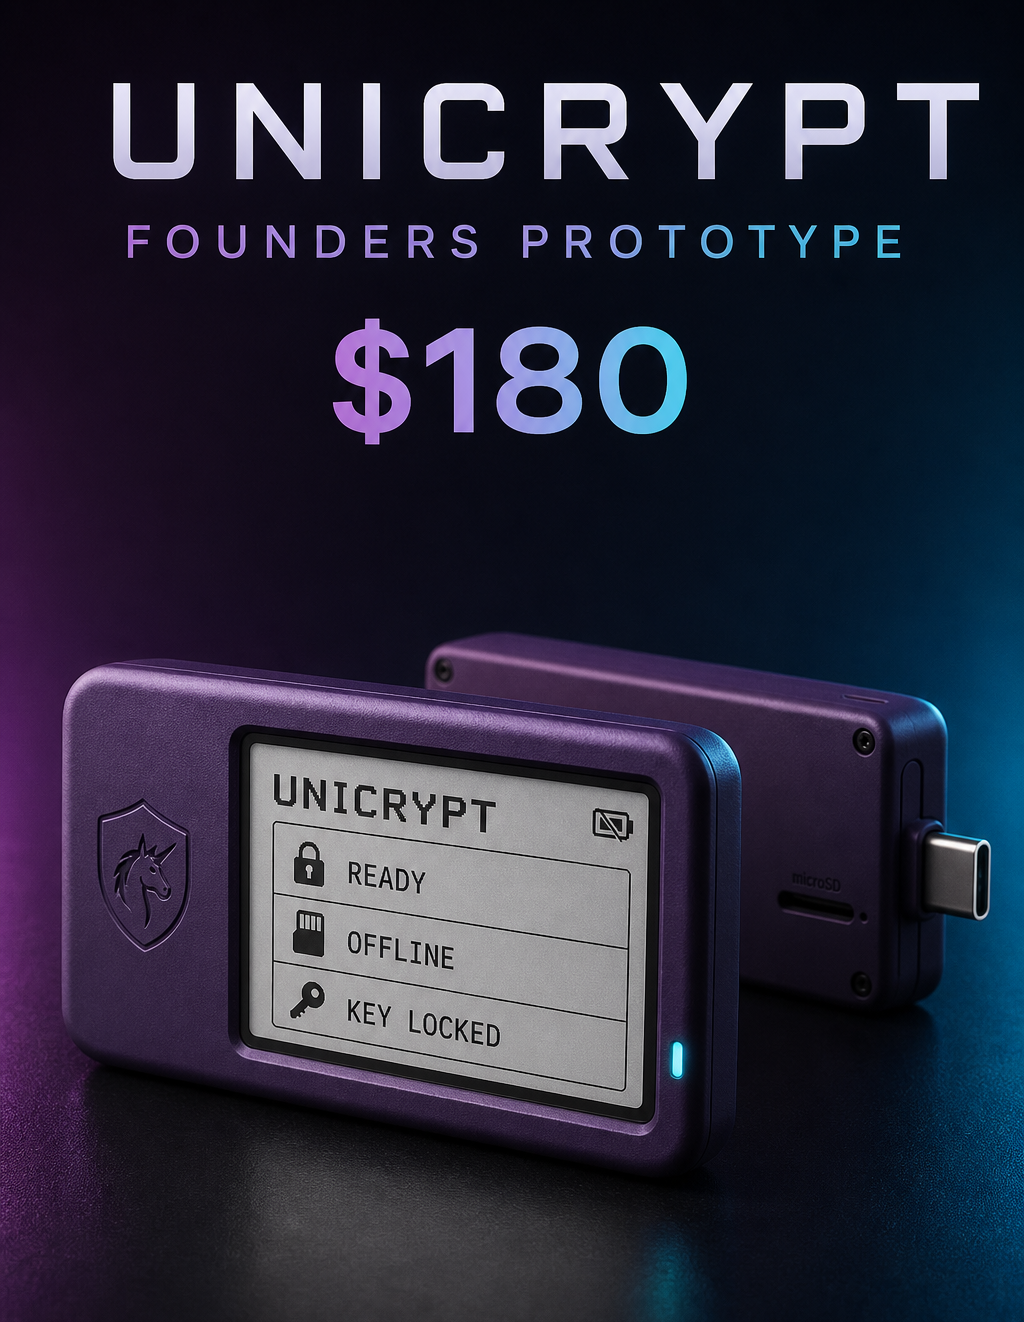
UniCrypt is a self-contained file compression and encryption appliance. The computer supplies files through a local browser interface; the device performs the work and keeps its master-key material off the host.
Experimental hardware prototype—not yet a certified security product or a retail offer.
01 / THE IDEA
UniCrypt creates its own local Wi-Fi network and serves a browser interface at a private address. No desktop application is installed, and the prototype does not require an internet connection.
The ESP32-C6 streams compression and AES-256-GCM authenticated encryption to microSD. A separate Digispark/ATtiny85 component contributes the physical secret used to derive vault keys.
02 / PROTOTYPE ARCHITECTURE
Private Wi-Fi access point, browser UI, streaming DEFLATE, AES-256-GCM, randomness, hashing, and storage control.
The removable ATtiny85 prototype carries EEPROM secret material used in per-vault key derivation.
Stores originals when requested, encrypted/compressed outputs, restored files, and operation logs without keys or contents.
Files move in bounded sequential chunks through a local-only interface, avoiding whole-file buffering on constrained hardware.
03 / SECURITY REALITY
AES-256-GCM can detect ciphertext alteration, and each encrypted file uses a fresh salt and nonce. The planned device does not overwrite source files.
The founders prototype is not a certified security product. The ATtiny85 is not a secure element, physical extraction is outside the current threat model, and losing or reprovisioning the hardware key can make encrypted files unrecoverable.
04 / SEED DEVELOPMENT
UniCrypt gives Tethered Unicorn Labs a tangible hardware complement to Unicorn Forge: one product coordinates private intelligence, while the other explores private handling of sensitive files.
Finalize board selection, power delivery, enclosure, storage, physical-key interface, and a secure-element migration path.
Failure recovery, authenticated file format, key lifecycle, reproducible builds, dependency review, and destructive-test coverage.
Independent design review, attack-surface testing, documented limitations, recovery guidance, and pilot threat modeling.
Small-batch prototypes, manufacturing estimates, user testing, accessibility, legal review, packaging, and support documentation.
This page describes an experimental founders prototype and forward-looking development plans. Product design, component selection, security properties, pricing, timelines, and commercial availability may change after engineering and independent review. Nothing here is an offer to sell securities or a guarantee of performance.